
Welcome to CSIT Technology Conference (TechCon) 2026!
CSIT proudly presents TechCon 2026 - a closed-door, by-invitation-only technical conference where the Singapore government and global industry cyber practitioners and experts converge.
In its 4th annual edition, TechCon 2026 deep dives into the disruption of digital threats and how AI impacts cybersecurity. Guest speakers will provide unique insights on how organisations can address these pressing issues.
TechCon 2026 is more than a conference. It brings together a community of practitioners and experts in digital defence, presenting a unique opportunity to network with peers who shape the future of cyber resilience and innovation. Exchange insights, challenge assumptions and build partnerships to collectively defend against ever-evolving cyber threats.

Morning Sessions
9:00 AM | Welcome Address
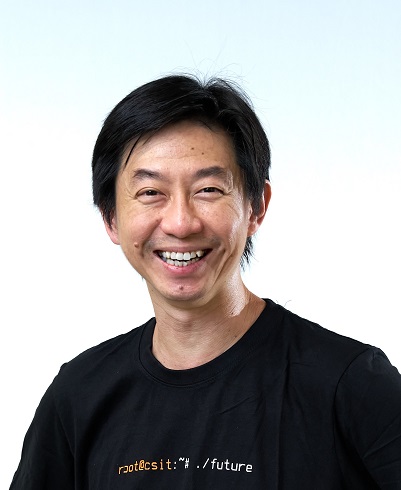
Darren Teo
Chief Executive, CSIT
9:05 AM | Keynote Address: 0-Days and Old Tricks
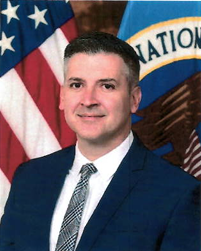
David Imbordino
Director, Cybersecurity Directorate, NSA
9:35 AM | Keynote Address: Security in the AI Era
As AI accelerates software delivery and empowers adversaries, organisations face a critical inflection point. Join Google Threat Intelligence VP Sandra Joyce as she explores the three core challenges shaping security today: protecting code generated at unprecedented velocity, safeguarding high-value AI workloads from theft and abuse, and withstanding automated adversaries operating faster than any human team can react.
This session will unpack why traditional approaches are unsustainable against autonomous threats, before outlining how defenders can evolve their security posture to regain the advantage.
Sandra Joyce
Vice President, Google Threat Intelligence
10:05 AM | The Adversary Evolved: AI is Reshaping the Threat Landscape
Adversaries are no longer just adopting new tools—they are operationalising AI to move faster, strike harder, and evade detection with unprecedented sophistication. In this session, Adam Meyers, SVP of Counter Adversary Operations at CrowdStrike, traces the evolution of AI-enabled adversary tradecraft—from early automation to ML-assisted reconnaissance, through today's GenAI-powered operations running at machine speed.
Drawing on real-world intelligence, Adam will examine how threat actors leverage LLMs for hyper-personalised phishing, AI voice synthesis for identity deception, and automated tools to accelerate vulnerability exploitation—illustrated through CrowdStrike's tracking of Evasive Adversaries.
The session closes with a focused look at Singapore's evolving threat landscape—its unique exposure as a regional financial and diplomatic hub—and the actionable defensive strategies organisations must adopt to stay ahead of the AI-enabled adversary.
Adam Meyers
SVP, Counter Adversary Operations, CrowdStrike
10:35 AM | Morning Break
11:05 AM | From National Strategy to the Kill Chain: China's AI Ambitions and the Weaponisation of AI by State-Nexus Threat Actors
Charles Li
Chief Analyst, TeamT5
11:35 AM | Panel Discussion
Sean Seah
Director, Mobile and Cloud Security, CSIT (Moderator)
12:30 PM | Lunch
Afternoon Sessions
2:00 PM | A Vulnerability Researcher's Guide to the Vulnpocalypse, 2024-2026
Since the start of 2026, AI agents have completely reshaped the landscape of vulnerability discovery and sent defenders scrambling to patch an unprecedented wave of AI-discovered vulnerabilities before attackers—often running their own AI agents—could exploit them. This talk will trace how the frontier models' cybersecurity capabilities grew from "barely usable" in mid-2024 to "nearly superhuman" today, from our perspective building AI agents for web penetration testing as well as our newer work finding vulnerabilities in widely deployed, hardened software like Google Chrome. Brendan will conclude by sketching how he thinks offence/defence balance will play out as we go deeper into the ongoing "vulnpocalypse".
Brendan Dolan-Gavitt
Distinguished Engineer, XBOW
2:30 PM | Security in the Age of Frontier AI: Hands-On with Mythos and Modern Defence
The release of frontier AI models has fundamentally altered the cyber battlefield, shifting the advantage toward those who can execute at machine speed. While defenders look to AI to streamline operations, threat actors are weaponizing these same large-scale models to dismantle traditional security perimeters.
In this session, Unit 42 experts lift the hood on the next generation of automated cyber warfare. Sharing exclusive, real-world red team findings from hands-on testing with Mythos, this presentation reveals exactly what happens when frontier AI is unleashed in an offensive context. We will demonstrate how advanced models provide a dangerous step-function improvement for attackers, drastically lowering the barrier to entry while scaling highly sophisticated, multi-stage attacks.
Attendees will get an inside look at how Mythos like models dynamically authors zero-day exploits, adapts to target environments on the fly, and systematically bypasses legacy security controls that rely on static signatures and human-speed response.
Beyond the threat landscape, this session is a practical blueprint for resilience. You will walk away with actionable, field-tested strategies to modernize your defence and neutralize AI-driven threats before they hit your production environment.
Shay Nahari
VP Offensive Security Services, Unit 42, Palo Alto Networks
3:00 PM | Disruption: How to Make Life Miserable for Cybercrime Groups
Cybersecurity has traditionally focused on detecting and responding to attacks after adversaries have already taken action. This session explores a more proactive approach: continuously identifying, disrupting, and increasing the operational cost of cybercriminal infrastructure before attacks succeed. Attendees will learn practical strategies for making it harder, slower, and more expensive for threat actors to operate, and why persistent disruption can be one of the most effective forms of cyber defence.
Ken Bagnall
Founder and CEO, Silent Push
3:30 PM | Afternoon Break
4:00 PM | What if the Key to Uncovering a Nation-State Operation was Hidden Inside a Compromised Edge Device?
In this session, we dive into our investigation of Ink Dragon, a China-nexus APT targeting high-profile organisations across East Asia and Europe. We’ll show how deep analysis of a compromised edge device allowed us to reconstruct the attacker’s operation, from initial access and lateral movement to credential collection and exfiltration.
We’ll then go inside FinalDraft, Ink Dragon’s sophisticated backdoor, and show how we fully reverse engineered its latest obfuscated version to uncover new capabilities and cloud-based C2 channels. Along the way, we’ll demonstrate how AI-assisted workflows, including IDA MCP, became part of the investigation and reverse-engineering process, helping us navigate complex code, accelerate analysis, connect findings, and ultimately build a clearer picture of how the threat actor operated end-to-end.
Moshe Marelus
Malware & Threat Intelligence Researcher, Check Point
4:30 PM | Turning Black-box Footholds into White-box Analysis
We will share insights on how black-box exploitation can be pivoted into white-box analysis to uncover deeper and more impactful vulnerabilities, as well as how manual and AI-assisted workflows can work hand in hand to accelerate offence-informed defences. We will illustrate these insights drawn from our experiences in pen-testing web applications and security appliances.
Sng Peng Boon
Lead Technical Specialist, CSIT
Poon Jia Qi
Security Researcher, CSIT
5:00 PM | From Counting to Countering: Tracking and Disrupting the Chinese Phishing-as-a-Service Ecosystem
Chinese Phishing-as-a-Service (PhaaS) has industrialised cybercrime, enabling novice actors to deploy sophisticated credential and 2FA harvesting campaigns at scale. While defenders traditionally rely on reactive domain takedowns, these measures often devolve into an endless game of Whac-A-Mole against resilient transnational adversaries.
This session provides an inside look at the Chinese PhaaS ecosystem, tracking 19+ operations and assessing their direct impact on Singapore through localised transport, logistics, and public sector lures. We explore adversary tactics ranging from Telegram escrow markets to localised causeway SMS blasters.
Moving from counting threats to countering them, we present a case study on Google’s civil litigation against the Outsider PhaaS syndicate. Attendees will learn how threat intelligence was translated into actionable courtroom evidence to seize infrastructure, disable exfiltration channels, and establish a cross-functional legal and technical disruption framework.
Roberto Martinez
Senior Analyst, Google Threat Intelligence

MC
Senior Analyst, Google Threat Intelligence
5:30 PM | End of TechCon 2026
Frequently Asked Questions
1. What time should I arrive?
2. Can I take photos or videos of the presentation material?
3. Can I share general photos of the event on social media?
4. Can I share information obtained from the conference?
5. What is the dress code?
6. Will refreshments be provided?
7. Can I give my seat to someone else?
8. Attendance etiquette
Getting there
Information on chartered bus services and nearby parking options for TechCon 2026.
View transport information here
(for registered guests only)